Quantum fixes protect Bitcoin, but legit owners risk lockout
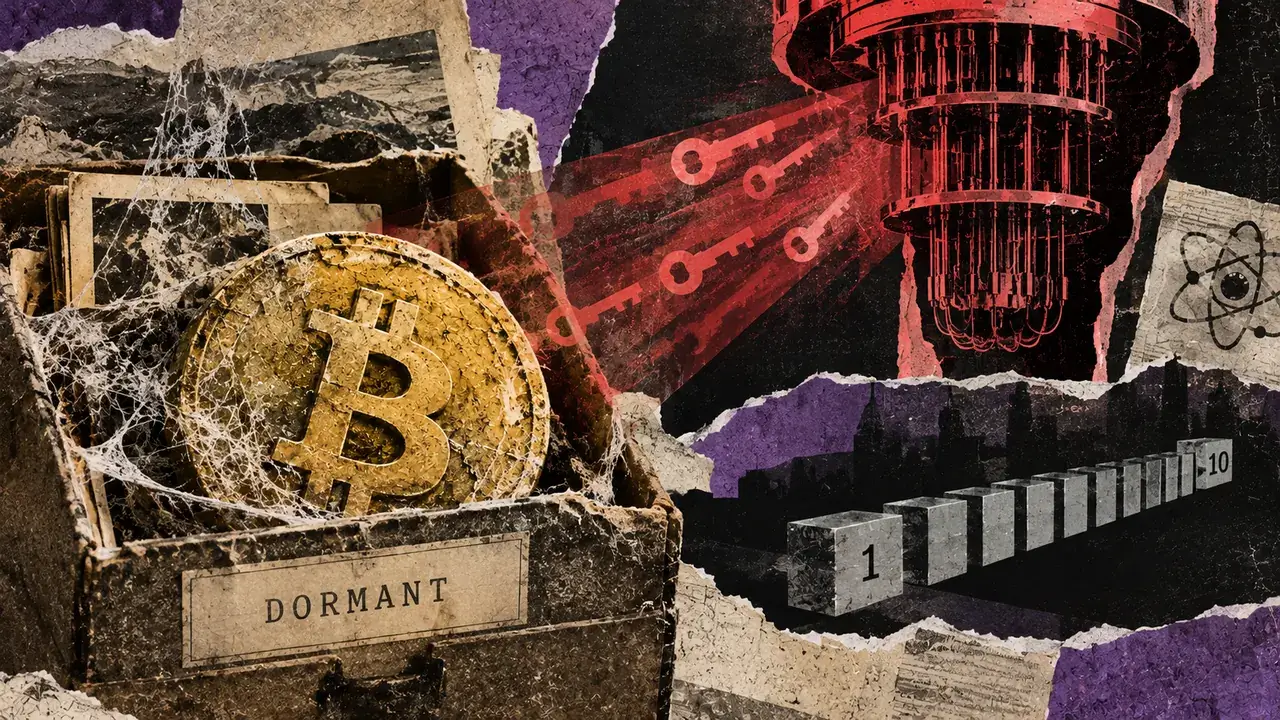
Crypto investor Nic Carter’s worst-case quantum scenario consists of a hostile actor recovering the keys to dormant Bitcoin, then broadcasting a wave of spends across 10 blocks.
In his Oct. 13 interview with Luke Martin, Carter says early coins moving together could shake confidence in the network.
The stakes extend beyond choosing stronger cryptography. Glassnode’s May 20 analysis identified 6.04 million BTC, or 30.2% of then-issued supply, with public keys already exposed.
The scenario assumes a future quantum machine capable of breaking Bitcoin’s key cryptography. Google’s published research models future resources for such an attack, and Bitcoin key recovery remains undemonstrated in that work. Large early outputs can nevertheless make a rapid transfer possible on block-space grounds.
Can millions of BTC fit in 10 blocks?
A sufficiently powerful quantum computer could use Shor’s algorithm to recover private keys from exposed public keys, gaining the ability to authorize spending. Early pay-to-public-key (P2PK) outputs reveal those keys directly.
An attacker could work privately, withholding transactions until ready, as Bitcoin Improvement Proposal 361 (BIP-361) explains.
Bitcoin tracks funds in individual unspent outputs, each with its own spending conditions, and a transfer’s size depends on how many outputs it consumes and their type.
Consider an explicitly hypothetical set of 50,000 early outputs holding 50 BTC each, totaling 2.5 million BTC altogether. Using the Bitcoin developer reference’s P2PK input example, those inputs require about 5.7 million bytes, equivalent to 22.8 million weight units before transaction overhead.
Ten blocks have an aggregate ceiling of 40 million weight units under Bitcoin’s block-weight rules. With one compact receiving output per batch, the illustrative set fits beneath that ceiling, including overhead, when split into transactions below Bitcoin Core’s 400,000-unit standard weight limit.
An actual sweep’s block-space demand would depend on its particular outputs and spending requirements.
Fees, competing traffic, and miner decisions still determine inclusion. Confirmation follows only when miners include the transactions. With Bitcoin’s approximately 10-minute block interval, 10 blocks average roughly 100 minutes, with substantial variation.
Glassnode’s exposure measure includes active holdings whose keys became visible through earlier spending or address reuse, alongside structurally exposed outputs such as P2PK and Taproot.
Public-key exposure, holder inactivity and permanent key loss are separate questions, as is attribution to Satoshi Nakamoto.
In his May 21 analysis, security researcher Jameson Lopp estimated that about 2.6 million exposed BTC might be unable to migrate, using inactivity and known-entity labels as proxies.
A quantum sweep would transfer control of existing coins without creating additional issuance. A visible transfer could unsettle holders before a sale, while exchange responses and liquidity conditions would determine any subsequent market disruption.
Who could still prove Bitcoin ownership?
Keeping existing spending rules intact preserves the ability to spend with a valid key, including one a future attacker recovers. Restricting legacy signatures changes that bargain: owners who cannot migrate or meet rescue conditions could lose access.
Draft BIP-360 proposes Pay-to-Merkle-Root, a new output type without Taproot’s exposed key spending path. It would reduce long-exposure risk when keys stay hidden.
BIP-361 proposed phases would restrict new vulnerable destinations about three years after activation, then tighten legacy-signature spending through rescue conditions about two years later.
For comparison, Google’s 2029 target sets its own precautionary migration deadline.
One potential rescue relies on a parent secret in a wallet that uses hardened key derivation. An attacker recovering an individual spending key would ordinarily lack that additional secret. For bare P2PK outputs, the draft’s authors describe that kind of ownership proof as an unresolved problem.
Dan Robinson’s May 1 PACT concept explores advanced, private timestamps proving address control. Future rules could recognize that evidence after a legacy sunset, and its protection depends on the holder preparing before quantum key recovery becomes possible and preserving the proof, alongside standardization and adoption of future verification rules.
The February Hourglass V2 draft takes another approach: one P2PK spend and one BTC of net spending per block. Throttling would slow the outflow while constraining legitimate holders under the same rules.
These remain proposals and research concepts. Their trade-offs include continued exposure, restricted access, and unequal recovery options.
Under the BIP process, Bitcoin’s participants evaluate and adopt proposed changes through software and ecosystem acceptance.
Carter’s scenario brings the key choice into focus: safer destinations can protect holders who can move. Bitcoin’s community would still have to decide which claims to recognize when an ordinary signature can no longer distinguish an original holder from a quantum attacker.